See what the report will include.
Preview a fictional executive-summary page below. This is a sample page, not a complete report. The sections below describe what the standard assessment report includes.
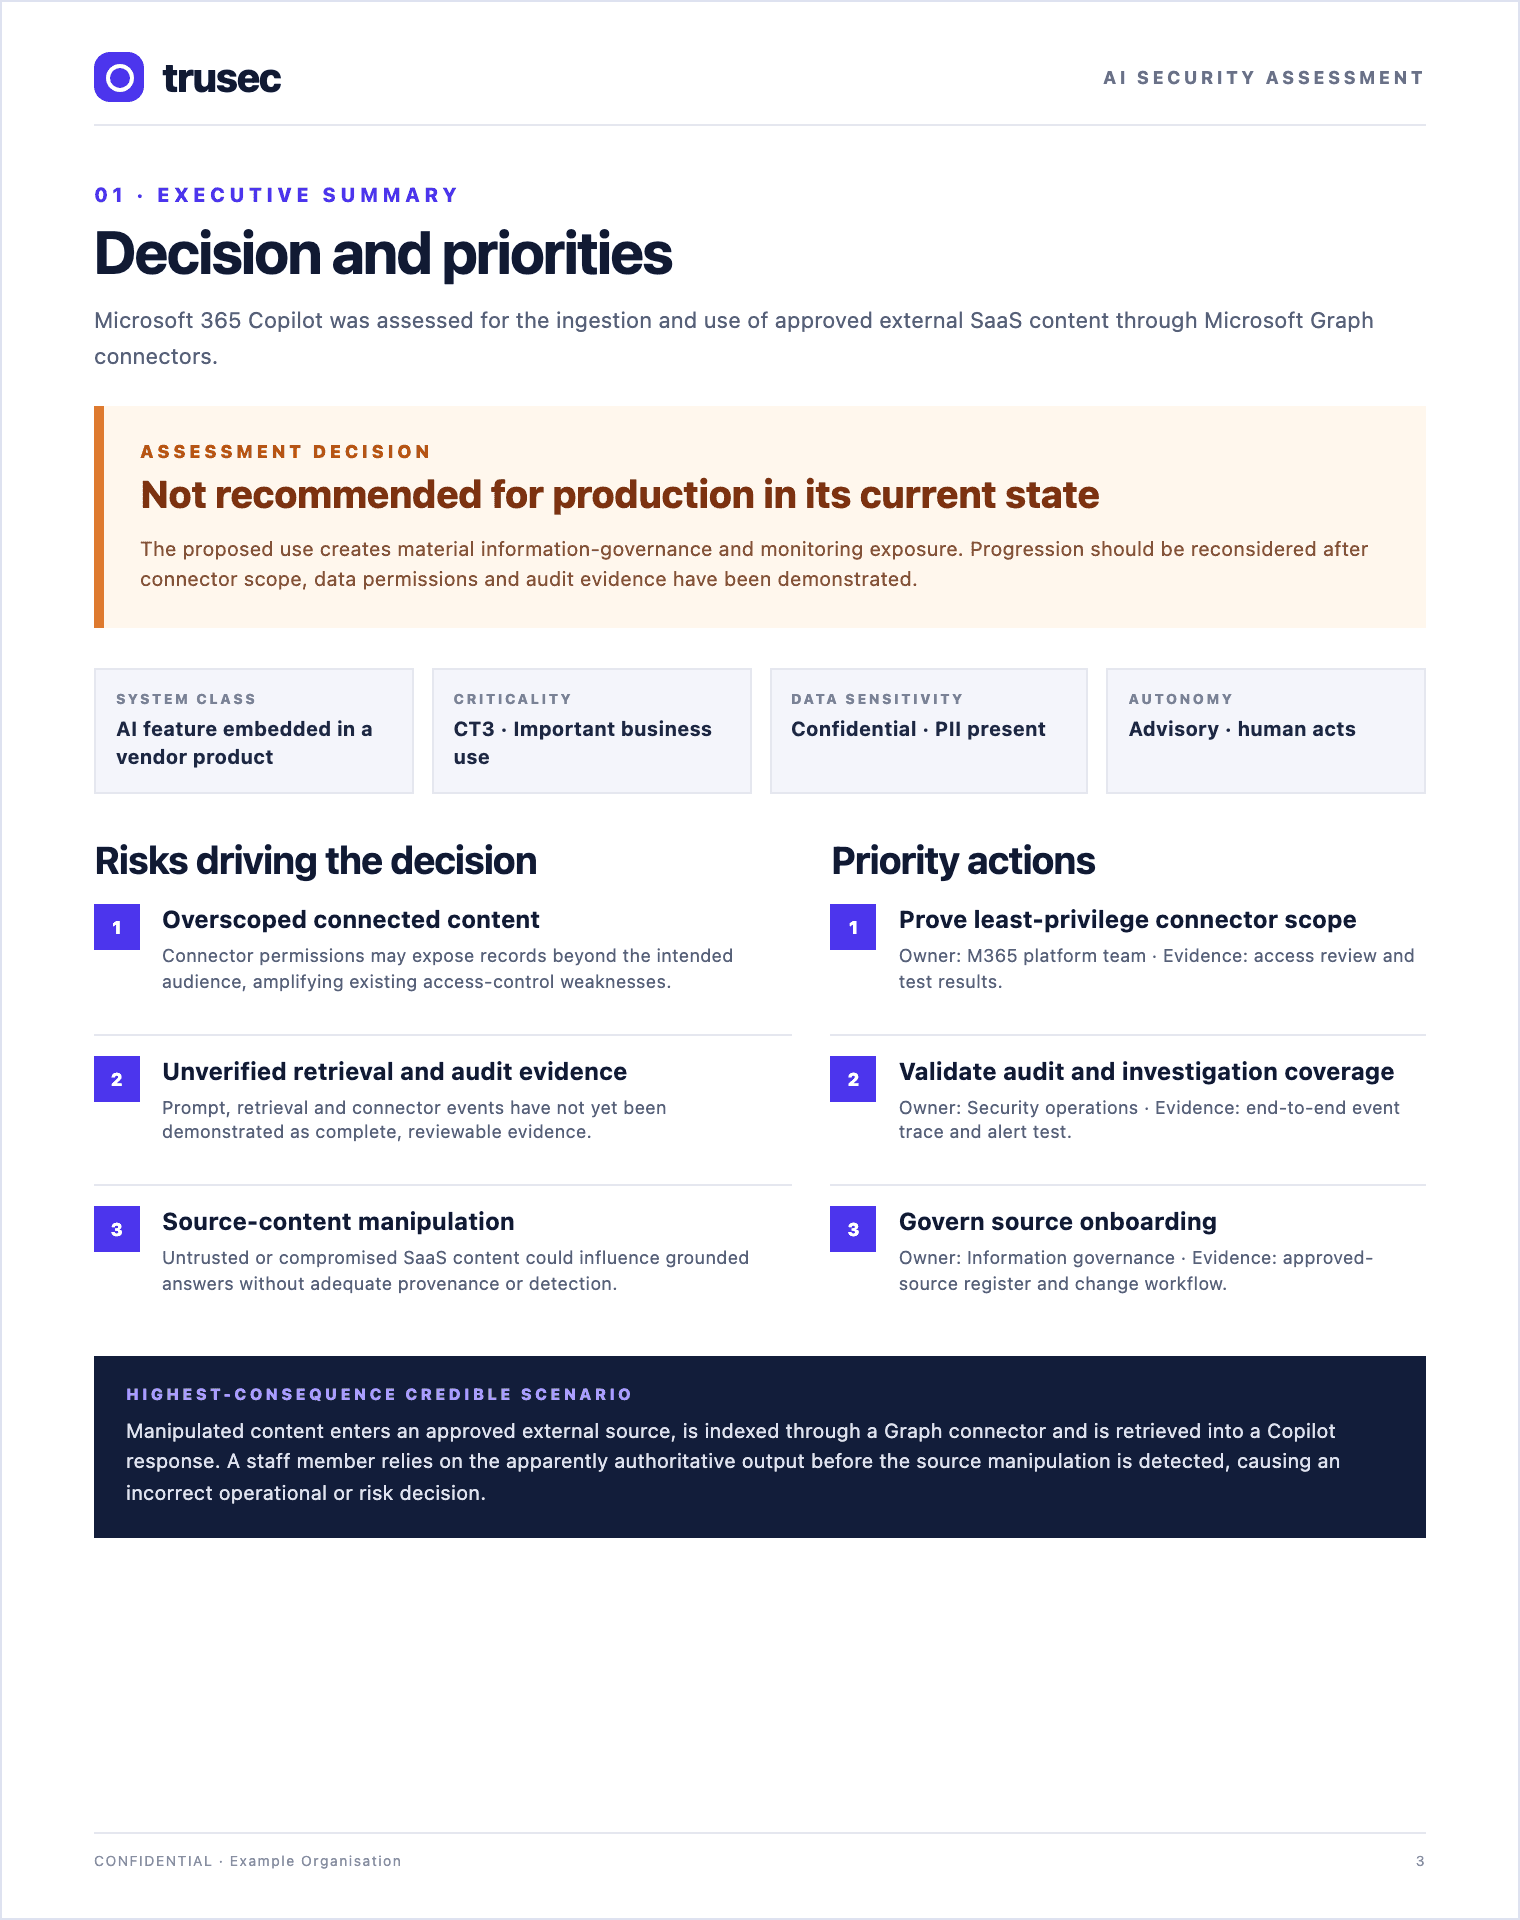
Sample page · Not a complete report
Enlarge sample page (opens in a new tab)Executive summary and readiness status
A concise view of the decision, material risks, launch blockers, and conditions that need attention.
Prioritised findings
Findings organised by severity and decision impact, with the supporting facts and assumptions made clear.
Threat model summary
The important assets, actors, trust boundaries, abuse paths, and AI-specific threat scenarios.
Control and evidence gaps
A practical view of missing or weak controls and the evidence still needed to support the decision.
Framework mappings
Relevant findings mapped to the applicable assessment frameworks where the evidence supports the mapping.
Remediation backlog
Prioritised actions, owners, and next steps that turn findings into a usable security work plan.
The report supports security and go-live decisions. It is not a penetration test, code review, certification, legal opinion, or assurance sign-off.